01
Assess Your Security Posture
Combine vulnerability findings, exposed assets, and scan evidence.
Compliance
Turn security assessments and findings into useful evidence for risk reviews, control mapping, and remediation planning.
How It Works
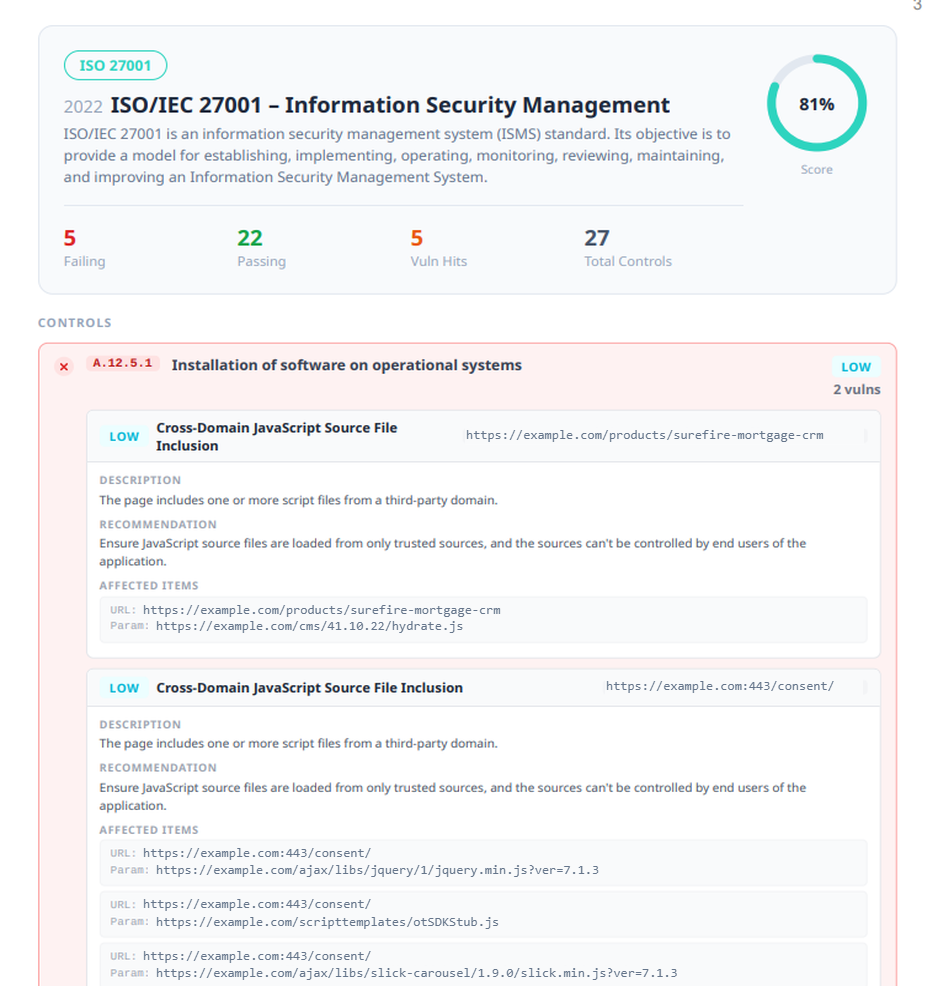
Organize assessment evidence, map findings to framework controls, identify gaps, and track remediation through structured reports.
Combine vulnerability findings, exposed assets, and scan evidence.
Connect assessment findings to applicable control requirements across selected security frameworks.
Highlight control-related weaknesses and missing evidence that need investigation or remediation.
Generate structured, framework-mapped findings reports to support security reviews and audits.
Track remediation and rescan findings to confirm open and resolved issues.
Security Reporting
Security reports provide a structured view of identified findings,
helping teams understand severity, track status, and focus
remediation efforts.
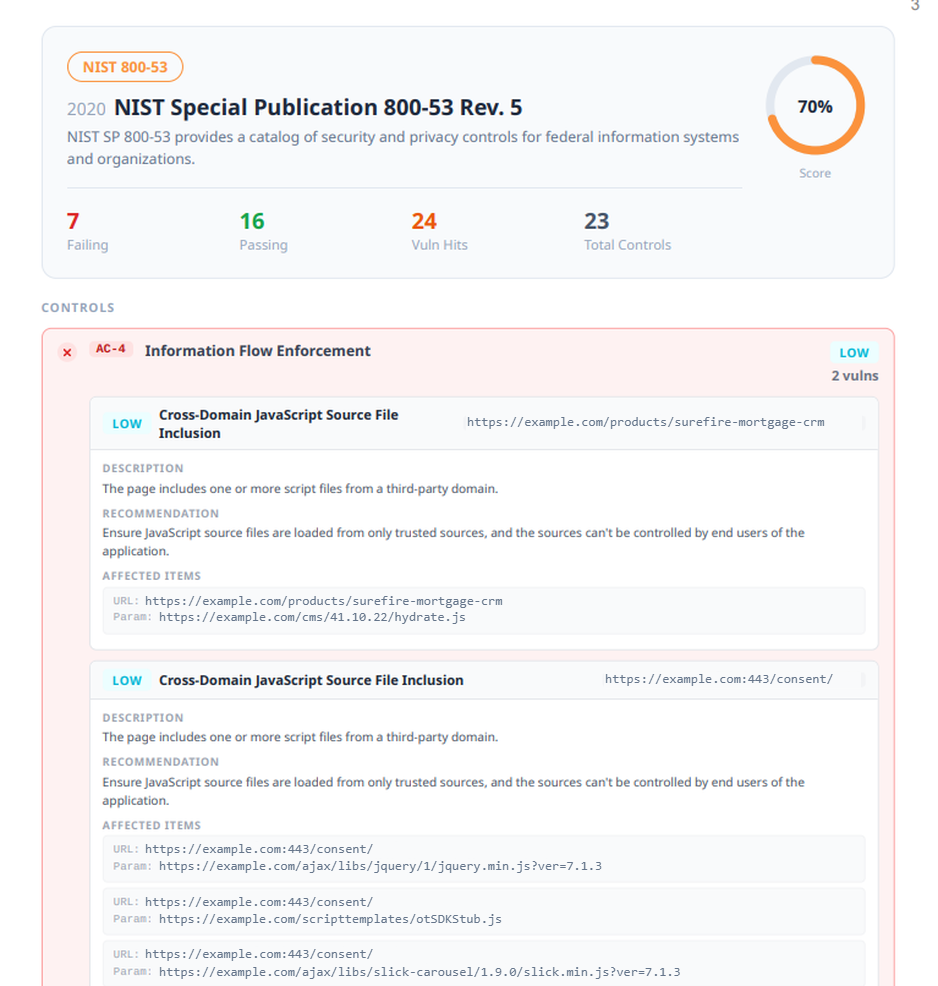
Review NIST SP 800-53 Rev. 5 control results, linked security findings, technical evidence, and remediation guidance.
See passing and failing security control checks.
Review vulnerabilities linked to unmet requirements.
Inspect affected URLs and supporting scan details.
Focus on issues mapped to failed control checks.
Discover exposures, assess vulnerabilities, investigate threats, and manage security findings across your digital environment.
Request a Demo