Vulnerable Images
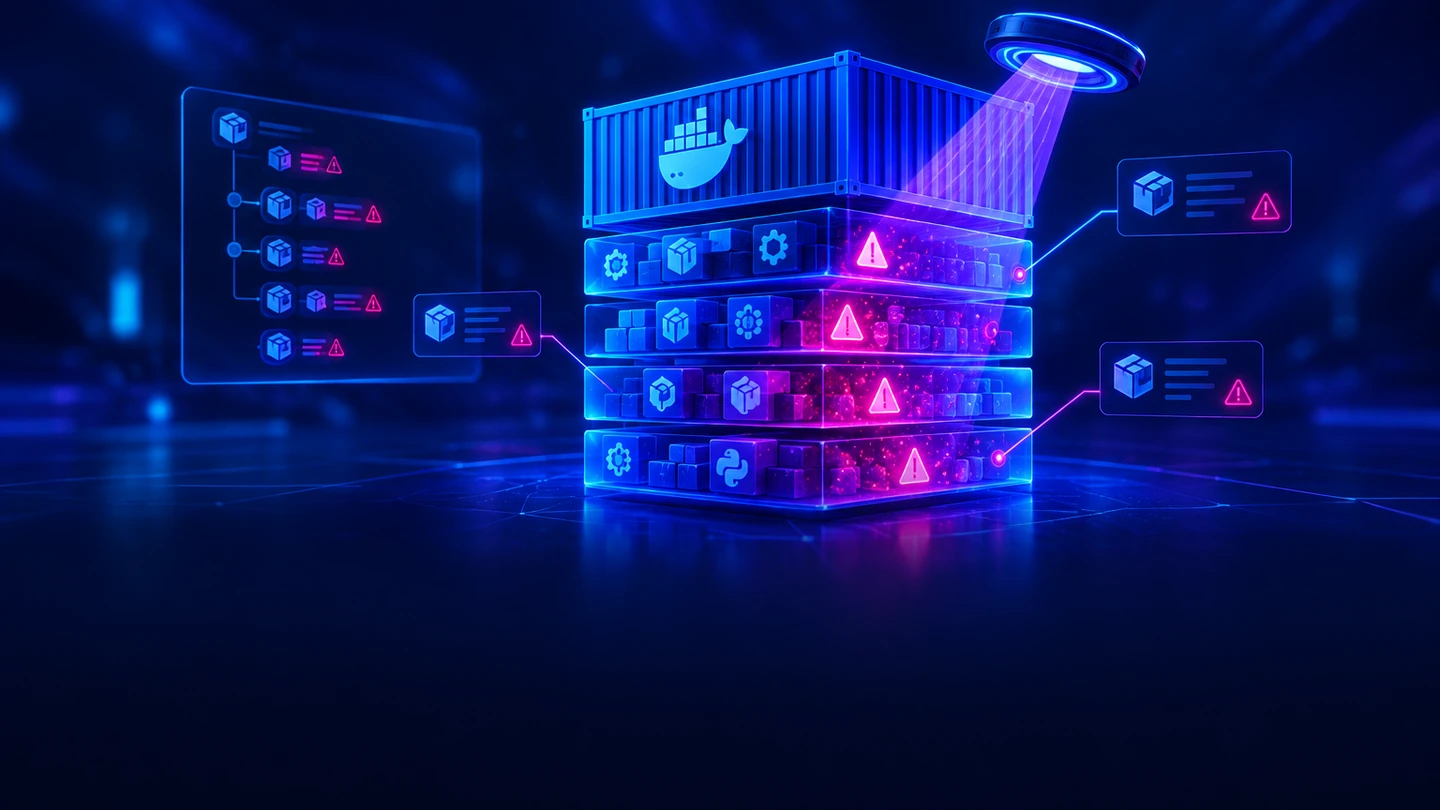
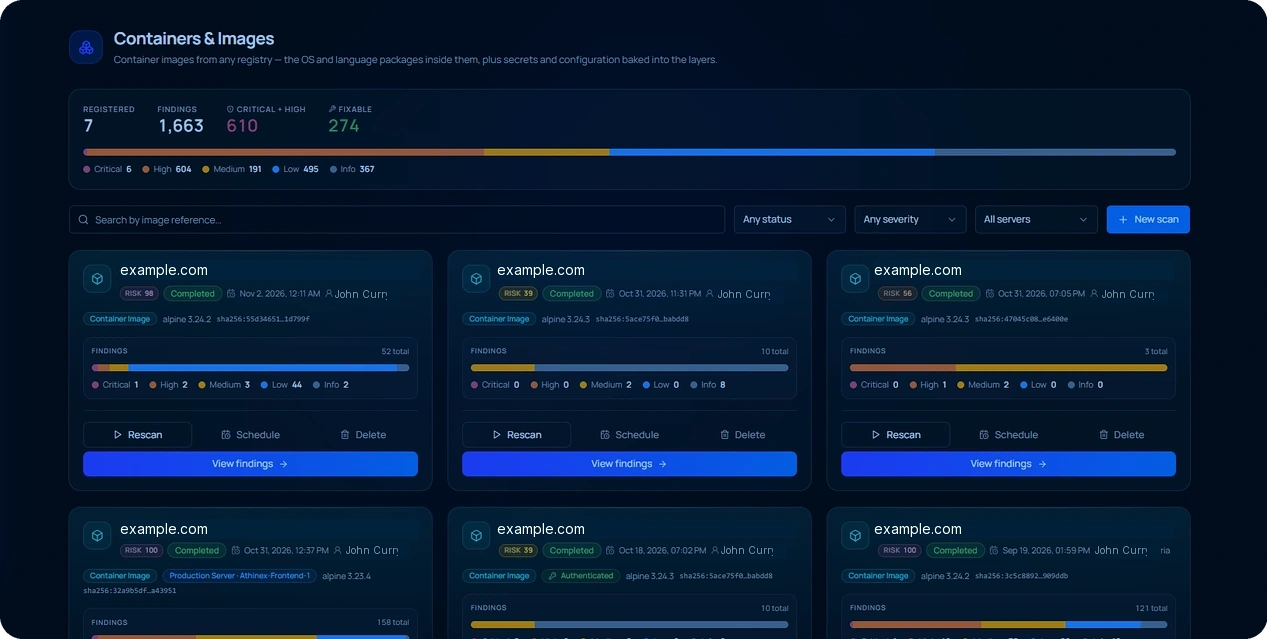
Container images can include known OS and dependency vulnerabilities.
Container & Infrastructure Security
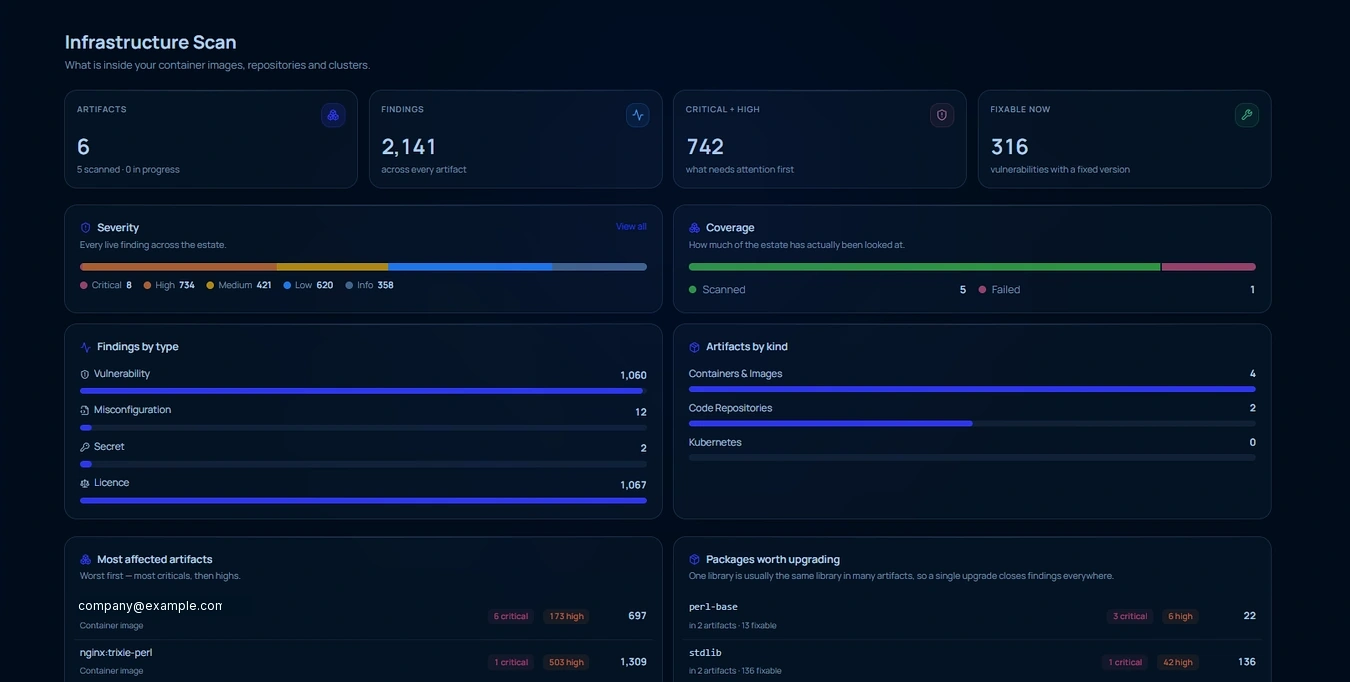
Assess Docker and OCI images, code repositories, and Kubernetes/OpenShift configurations with centrally managed security scanning.
The Challenge
Vulnerable dependencies, exposed secrets, insecure images, and misconfigured clusters create risk across the software delivery lifecycle.
“Visibility into images, repositories, and clusters makes security issues actionable.”
Container images can include known OS and dependency vulnerabilities.
Repositories may contain secrets and insecure infrastructure definitions.
Unsafe workload settings and broad permissions increase risk.
Remote hosts and private registries need centralized assessment.
How It Works
Athinex consolidates container, repository, and Kubernetes/OpenShift assessment workflows.
Select images, repositories, or clusters.
Connect remote Linux scanners.
Find CVEs, secrets, and configuration risks.
Review cluster settings and permissions.
Prioritize fixes and rescan updated assets.
The Solutions
Assess images, repositories, Kubernetes/OpenShift environments, and distributed workloads through a unified scanning workspace.
The Impact
Assess images, repositories, Kubernetes/OpenShift environments, and distributed workloads through a unified scanning workspace.
Assess images, repositories, Kubernetes/OpenShift environments, and distributed workloads through a unified scanning workspace.
FAQs
Answers About Container & Repository Scanning
Athinex analyzes a selected Docker or OCI image for vulnerable packages and other supported security findings.
Discover exposures, assess vulnerabilities, investigate threats, and manage security findings across your digital environment.
Request a Demo